SYNEDAT® · Trellix
Trellix – Endpoint, data and network security
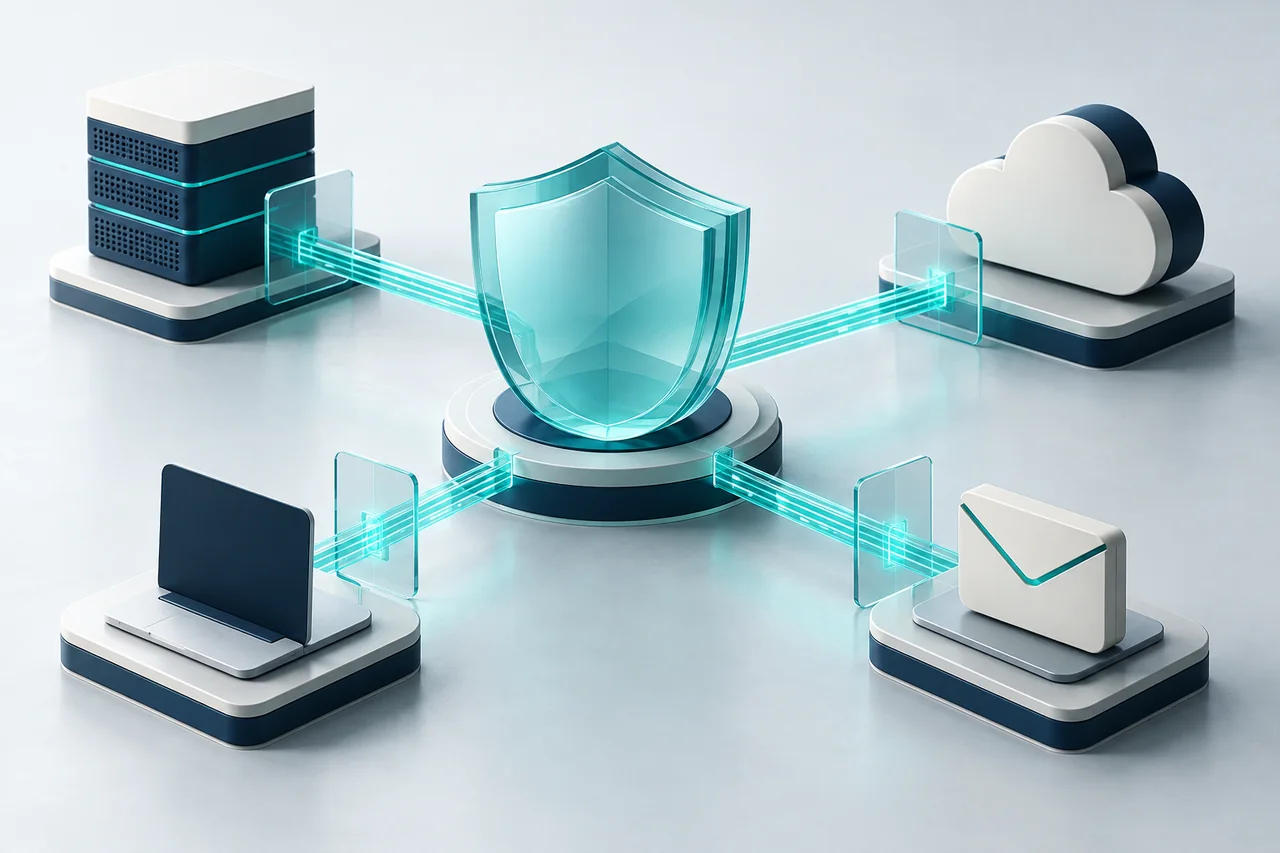
SYNEDAT maps the Trellix portfolio to protection and operating tasks. We plan endpoint protection, data controls and detection with shared ownership so events can be investigated and actions coordinated.
Which product family fits your needs?
Trellix Endpoint Security
Plan endpoint protection and investigation. SYNEDAT checks operating systems, existing agents and management roles.
Trellix Data Security
Select DLP and encryption for sensitive data flows. Policies are tested with business owners before blocking actions are enabled.
Trellix Network Security
Build visibility and detection at suitable network points. We check traffic feeds, capacity and investigation integration.
Trellix Helix
Bring security events and response workflows together. SYNEDAT defines data sources, case ownership and team handovers.
License scope, availability, term and support are reviewed for your project and specified in the quote.
Where the solution adds value
Renew endpoint protection in stages
A pilot group checks agent compatibility, policies and support cases. Migration is approved against measurable criteria with a documented rollback path.
Align data loss policies
SYNEDAT examines typical file and communication paths. Business exceptions, warnings and blocking are evaluated with data owners.
What matters when choosing
- Protection objectives and coverage
- Which applications, devices and data need protection? We compare capabilities against your attack surface and existing controls.
- Performance under real load
- Encryption, enabled security features and concurrent connections affect sizing. A pilot checks scenarios relevant to your operations.
- Operations and response
- Alerts need owners and clear response paths. We plan management, logging, updates and support with your team.
From selection to deployment
Define requirements and objectives
We review systems, users, security requirements and budget. The result is a reasoned selection with a defined scope.
Validate suitability in a pilot
For an agreed pilot, we define tests, acceptance criteria and responsibilities. You receive a documented basis for the investment decision.
Plan rollout and operations
We plan migration, configuration, handover and support together. Scope and responsibilities are agreed before rollout.
Downloads and manufacturer information
Explore your options with the linked service overviews and manufacturer documents. The language shown refers to each document.
-
Trellix Endpoint Security HX – Data Sheet (PDF; BlueAlly document library)
English
Open PDF: Trellix Endpoint Security HX – Data Sheet (PDF; BlueAlly document library) (English) ↗
Questions to help you decide
Must all Trellix products be deployed together?
No. SYNEDAT selects components for specific needs. Integrations, licenses and existing security tools are checked before deciding.
How do we limit disruption from new policies?
We test representative applications and start with monitoring policies where supported. Exceptions have owners and are reviewed regularly.
Is a firewall enough to protect our business?
A firewall controls network traffic. Identities, endpoints, email and applications need additional suitable controls. We assess existing coverage and prioritize useful additions.
Can we keep using existing security products?
We check interfaces, support status and overlaps. The aim is a coordinated architecture with clear responsibilities; replacing everything is not a prerequisite.
Can I request a demo or pilot first?
Yes. Tell us your intended use case. We will discuss available evaluation options, prerequisites, effort and acceptance criteria. A pilot is agreed separately before it starts.
What does SYNEDAT need for a quote?
Useful details include product family, deployment location, current systems, user or device count and target date. We clarify open points together and distinguish the product, implementation and ongoing services in the quote.
Can SYNEDAT help with rollout and ongoing operations?
We agree the services you need, such as architecture, integration, migration, documentation or operational support. Vendor support, response times and ongoing assistance are explicitly defined in the agreed scope.